
Do you know the telltale signs your WordPress site has been hacked? If you’re hanging out in the backend of WordPress only, it’s really easy to miss. Check out these key areas the next time you’re spending some time on your site security.
1. Check what users see when visiting your site
If your WordPress site looks like it’s supposed to at a quick glance, you might assume that everything is fine. But hackers don’t always look to take down sites. More often than not, they look for sites to do their dirty work for them. This is especially true of smaller sites that don’t belong to a huge company or celebrity.
The “dirty work” they want help doing could be installing malware/viruses on site visitor’s computers or hosting links to spam sites. The things you’ll want to watch out for on the front-end of your site (the part that site visitors see) are:
- Pop-ups that you didn’t install
- Random characters at the very top or bottom corners of your site (usually less than 5 characters in a small basic font)
- Images that link even though you didn’t set them to
- Injected links (links within your blog or page content) to spam sites
Make sure to view the site as your visitors do! Log out of the dashboard or view it in a new browser because some hackers are smart enough to hide the bad content from logged in users.
How to remove malware from a hacked WordPress site
Removing malware from a site often requires knowing your way around SFTP, PHP files + the mySQL database. Many hackers will inject malicious code into theme or plugin files that blend in with what existed before. If you know exactly when they gained access, you can restore the site to a previous backup + then increase your site security to hopefully prevent it from happening again.
- Add 2FA to your login process
- Hide your login screen
- Keep your site up to date
- Remove users that no longer access the site
- Reduce the number of admins
If you’re not sure when it happened, or it keeps happening, it’s best to bring in an expert. I’ve been removing malware from sites for 20+ years + know where to look. Your hosting company may also provide services to remove malware for an additional fee.
2. Review your own login and site stats
If you can’t log into your WordPress website but you are 110% confident that your username + password is correct, that is typically a sign that you’ve been hacked. (It’s a case of your login info being compromised + then changed so that the hacker can hijack your site.)
Now is the time to use the reset password link to make sure that your account email address wasn’t changed. If it was + you don’t get the reset password link, you’ll need a developer to help you reset the account information via the database.
Or maybe you can log into your site without issue, but you notice that your site stats are showing a huge increase in traffic from a seemingly random part of the world. Unless you have a travel blog post that went viral, this could mean that your site is loaded with injected links, or worse.
3. Google your own WordPress site
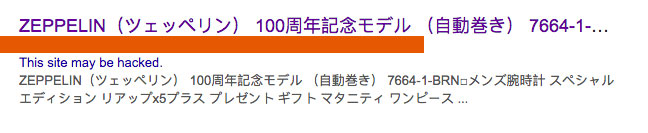
One of the easiest, albeit super depressing, ways to see if your site is hacked is by asking google.
To do this, head to google.com + type in your business name (not the URL). For example, I would type in tiny blue orange. Google is on top of their game. If your site has been hacked for some time, you’ll see “This site may be hacked.” below your link.
4. Scan your site using Sucuri
Another easy way to tell if your WordPress website has been compromised is to have it scanned by a company that specializes in this stuff. My favorite resource for that is Sucuri because they offer a free scanning tool. Simply type in your URL + run a scan. The results will share if you have malware, injected spam, or defacements. They’ll also share if you are on a blacklist for any search engine.
FYI – almost every WordPress site will be flagged with a risk on their website firewall. This is Sucuri’s way of selling their services from the free tool they are providing. Don’t stress too much about this warning. Instead, focus on whether or not your site has malware +/or has been blacklisted by search engines.
If your site was listed as hacked by Google, you’ll want to use Search Console to list what you did to fix it + request indexing of your homepage. That will get the warning removed as soon as possible, though never as quickly as we’d like to see it gone.

Get your hacked WordPress site back (and improve your security)
If you’ve been hacked, I’ve got a blog post with step by step instructions for you to take. Otherwise you can reach out to your web developer, hosting company or us for help.
If your site comes up clean + free of issues, the next step is to take the free WordPress security assessment. That way you can take care of any vulnerabilities your site has to avoid being another hacked WordPress site statistic.
And if the idea of being hacked scares the yoga pants off of you, let’s talk about your WordPress hosting options. We offer managed WordPress hosting which means your site is pampered with speedy + secure servers. In fact, we guarantee that if your site does get hacked on our servers, we will fix it for free. How much would that help you sleep at night?!